Introduction
Your finance team closes the books, only to find a cluster of software subscriptions and consulting fees that nobody recognized. The money left the company, but it never passed through an approved purchasing channel. This is maverick spend, and it creates a blind spot for finance teams, making budgets harder to forecast and control, often remaining undetected for months until a department overspends.
Traditional controls react at the point of purchase, blocking a transaction after an employee has already decided what to buy. That approach slows teams down and invites workarounds. An AI intelligence layer flips the model. It analyzes procurement data and contract signals post-signature to detect patterns of unauthorized buying, so you can prevent the next occurrence without crippling business speed.
What follows is a practical, seven-step framework for moving from a reactive policy stance to an interconnected ecosystem of data, AI, and proactive governance. You will learn how to define the problem with precision, connect the core data sources that matter, and embed intelligent policy gates that stop maverick spend before it starts.
Key Takeaways
Controlling maverick spend demands a shift from reactive blocking to an AI-augmented intelligence layer that spots non-compliance early. Here are the core principles that anchor the framework:
- Data-driven taxonomy: Maverick spend is a set of distinct breach types, unauthorized vendors, bypassed approvals, rogue p-card use, that require classification before intervention.
- Core data triad: Contracts, vendor master records, and purchasing logs must be unified into a single source of truth. AI operating on siloed data generates noise, not insight.
- AI as an intelligence layer: Rule-based ERP blocks stop at the transaction. AI analyzes post-signature patterns and invoice line-items against contract clauses to predict and flag future off-policy behavior.
- Proactive policy gates: Dynamic, risk-scored approvals and guided buying channels replace blanket block rules that employees circumvent. You stop maverick spend without grinding operations to a halt.
- Process velocity as a metric: Success includes more than cost savings. Maverick spend rate, contract utilization, and user friction scores prove that control and speed can coexist.
Step 1: Define and Diagnose Maverick Spend with a Data-Driven Taxonomy
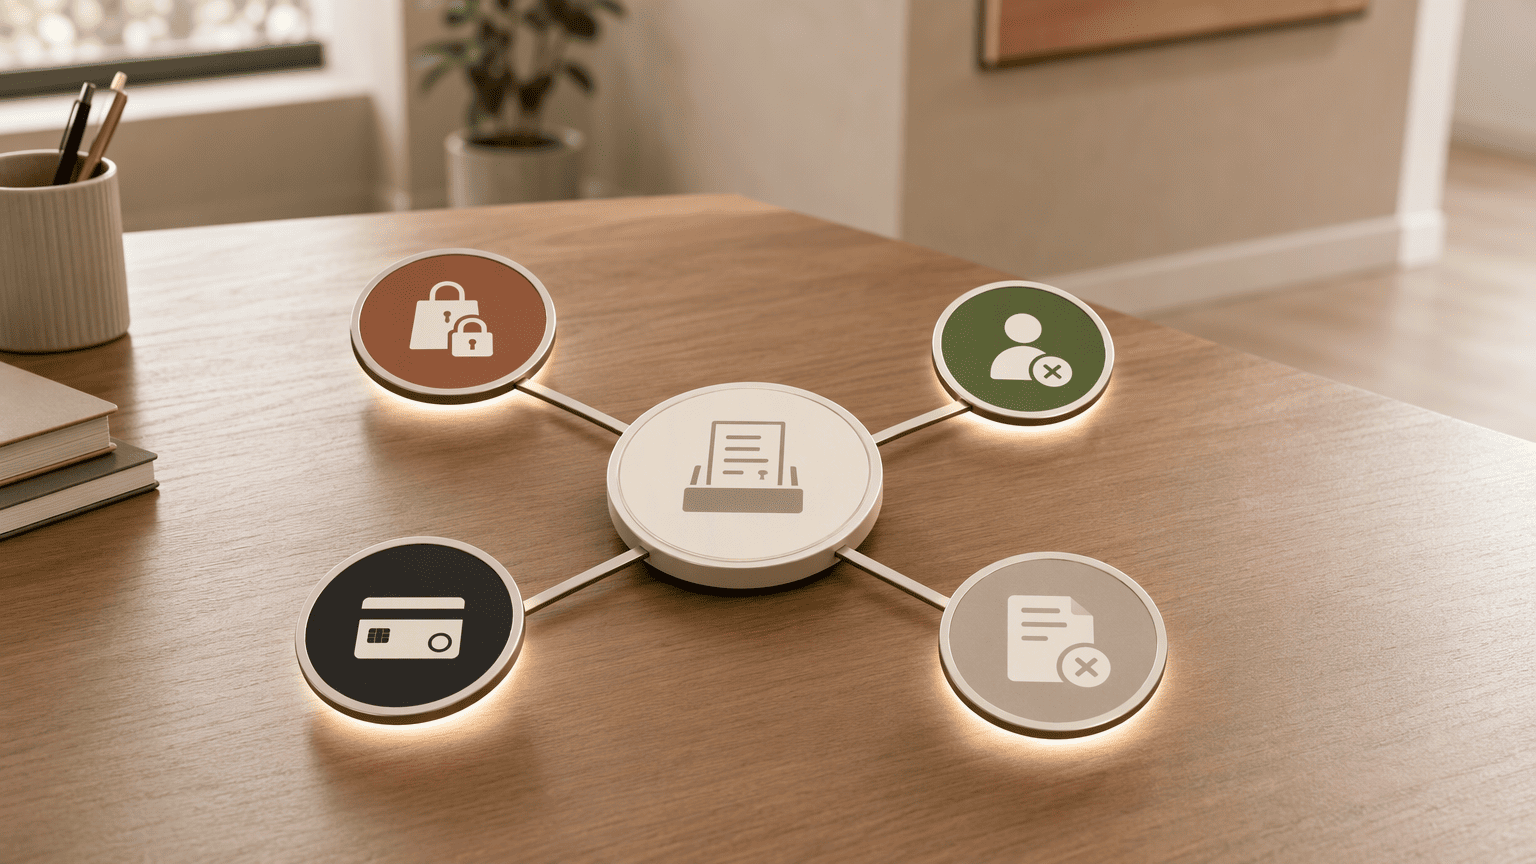
A vague awareness that off-policy buying exists will not power an AI initiative. You need a specific, measurable classification model built from historical transactional data, not gut feeling. Common examples of maverick spending include purchasing without required authorization, buying from an unapproved vendor, using a personal card instead of an approved company card, and failing to document a business purpose.
- Pull purchasing system logs: Export a full set of transaction records from your P2P and expense management systems for the trailing 18 months. Look for patterns like the same department repeatedly using a non-preferred supplier or card transactions with no associated purchase requisition.
- Categorize every non-compliant transaction: Tag each item against a simple breach taxonomy: unauthorized vendor, bypassed pre-approval, rogue p-card use, unapproved SaaS subscription, and out-of-policy travel. A single transaction may carry multiple tags.
- Pinpoint root-cause friction: Maverick spend usually points to friction or gaps in the purchasing process. For each tag cluster, identify what drove the behavior. A concentrated spike of unauthorized software subscriptions often traces back to a requisition workflow that takes two weeks to approve.
- Size the exposure: Aggregate the total dollar value and transaction count per breach category. This delivers a prioritized hit list for the AI intervention, so the AI focuses on blocking the most expensive breaches first.
Step 2: Connect the Core Data Triad, Contracts, Vendors, and Purchases
Maverick spend detection collapses when the three data sources that define compliance live in separate silos.
- Your approved vendor list sits in the ERP, active contract terms reside in the CLM, and actual purchasing logs stream through the P2P system.
- Running AI on any one of these alone produces a partial picture; the only accurate match happens when you force them together.
- Unifying these sources creates a single source of truth that answers a stark question: for every invoice line-item, is there an active contract with a pricing schedule that matches, and does the vendor appear on the approved list? When that connection is missing, you have found a maverick transaction.
- Building this linkage manually is slow, but modern AI extraction can ingest executed agreements from a CLM and map the named supplier to the real vendor record inside the ERP.
- Without this triad, an AI layer will surface thousands of false positives that exhaust your team or miss the exact pattern it was deployed to catch.
Step 3: Overlay an AI Intelligence Layer on Your Existing Tech Stack
A traditional ERP enforces policy reactively. It sees a purchase requisition for a non-preferred vendor and blocks it at checkout, creating a dead end that frustrates the buyer and often leads to a manual expense report as a workaround. An AI intelligence layer operates on a fundamentally different logic.
- It analyzes procurement data and contract signals post-signature to detect patterns of unauthorized buying, enabling proactive prevention.
- You augment your existing CLM and ERP investments with a layer that reads executed contract text and structured fields across both.
- When it finds an invoice charging a rate the contract never authorized, it flags that mismatch for a human to act on before the problem compounds.
- The AI learns from the full data triad and notices patterns invisible to a point-of-entry block.
- Poor contract management can cost companies up to 9% of annual revenue, often due to missed obligations and compliance lapses, according to World Commerce & Contracting.
- The intelligence layer also predicts future behavior by surfacing a risk score that triggers a guided approval path.
Step 4: Design Proactive, Not Reactive, Policy Gates
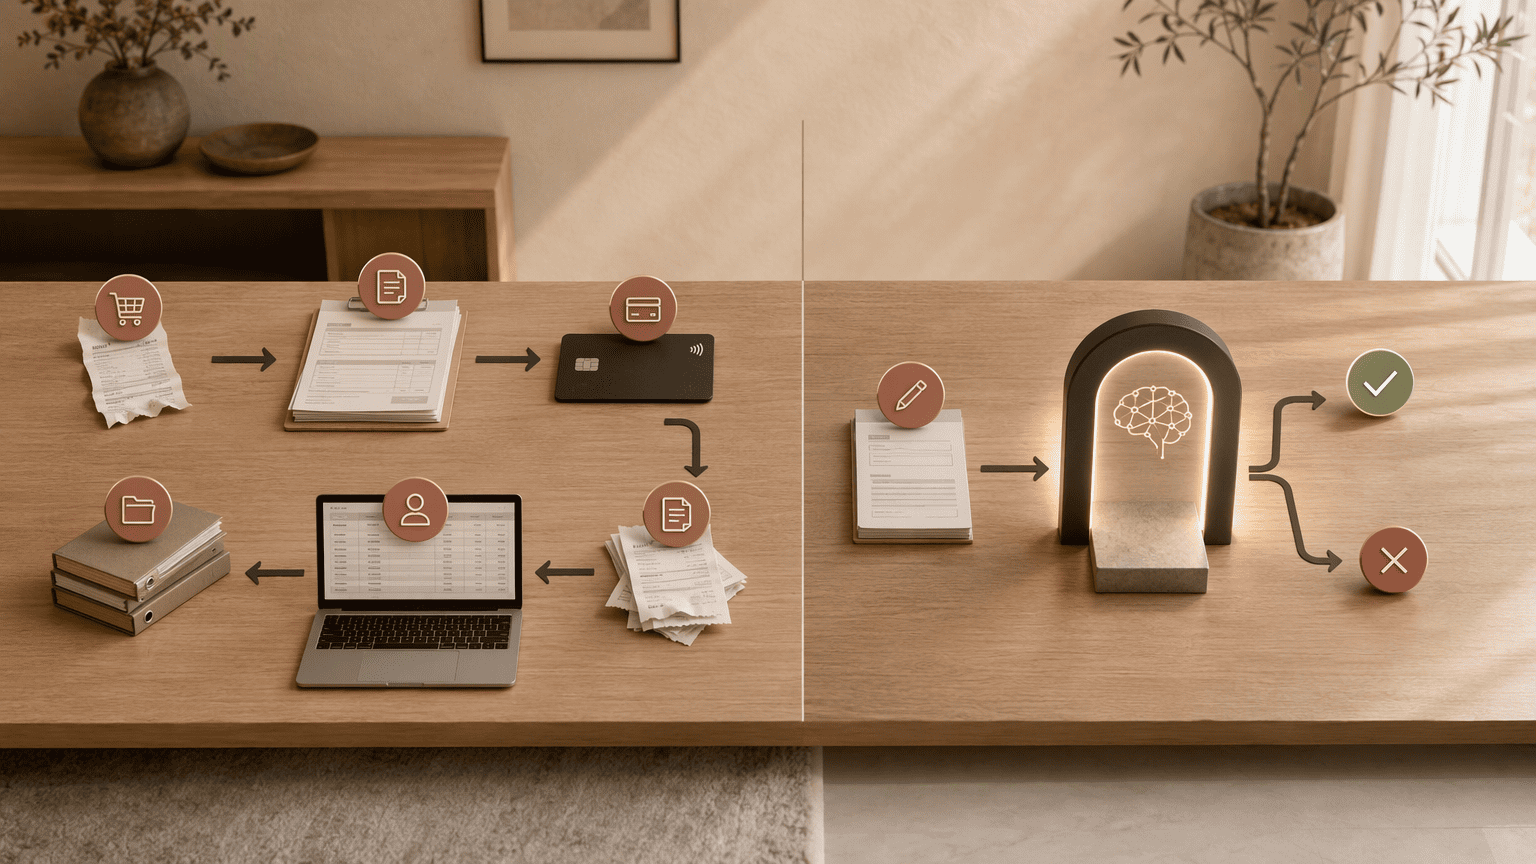
A blanket rule that blocks all unapproved purchases is easy to implement and even easier to bypass.
- Employees route the spend to a corporate card, load it into an expense report marked as a generic ‘consulting’ reimbursement, and the maverick transaction completes undetected.
- The policy gate failed because it was reactive, and the organization paid for the purchase plus the administrative work to hide it.
- Proactive gates use the AI risk score generated in Step 3 to intervene before the transaction finalizes.
- When a purchase requisition lands for a vendor not on the approved list, the system routes the request down one of two dynamic paths: a fast-track channel if the AI scores it as low risk or a just-in-time guided buying channel if the risk is high.
- In the guided path, the requisition auto-populates with a preferred supplier and contracted pricing pulled from the CLM, offering the employee a compliant option that takes less time than the rogue alternative.
Step 5: Surface Hidden Leverage by Grouping Related Agreements
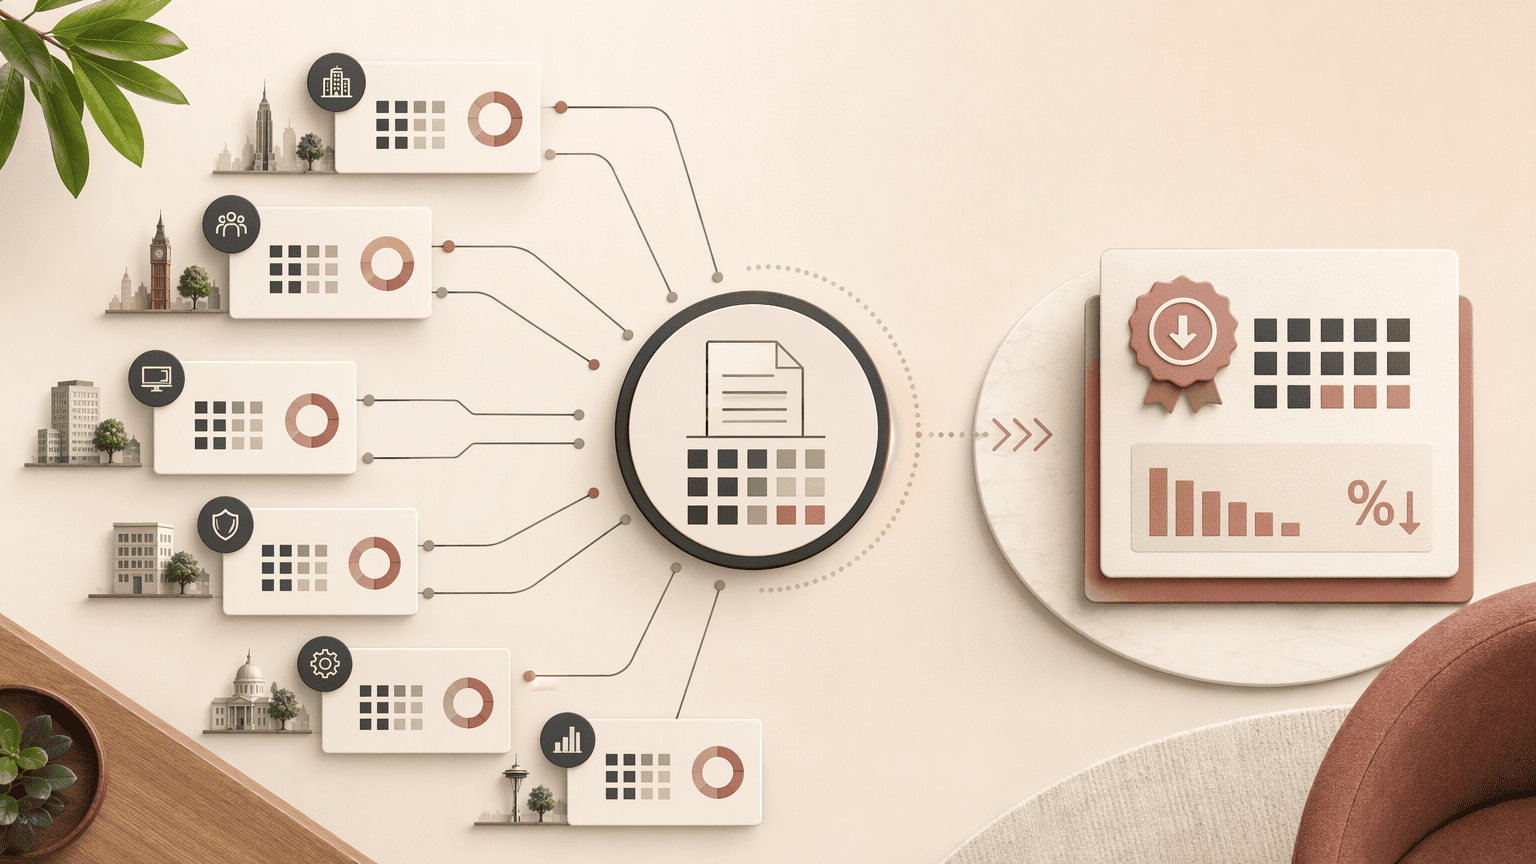
Maverick transactions rarely announce themselves as a coordinated pattern. A $150 monthly design-tool subscription purchased by marketing in New York looks unrelated to a nearly identical $150 subscription bought by the product team in Austin. Individually, neither breaches a dollar threshold that triggers a review. Clustered together by AI, they reveal that the company is paying two separate retail-rate subscriptions for a tool that a single enterprise license would cover at a steep discount.
AI clustering analysis groups these orphaned transactions by real vendor parentage and purchase sub-category, unmasking fragmented spend that manual reviews miss. The following table maps the shift from a fragmented view to a consolidated one:
| Spend Dimension | Fragmented View | Clustered AI View |
|---|---|---|
| Vendor identification | 18 distinct supplier names for what is actually 3 parent corporations | Real entity mapping across subsidiaries and DBAs |
| Pricing use | Each department negotiates its own rate; zero volume discount | Consolidated demand justifies a single enterprise agreement |
| Contract utilization | Active contracts exist but no one uses them because users are unaware | Matched transaction clusters flag where negotiated terms are being bypassed |
| Supplier rationalization | 40 technology vendors for overlapping SaaS categories | Actionable consolidation target of 15 strategic suppliers |
This exercise recovers volume discounts that were already negotiated but never activated because the spend was invisible. When you walk into a renewal conversation armed with a precise map of actual enterprise-wide consumption, you shift from a price-taker to a partner negotiating from reality.
Step 6: Embed Audit-Grade Data Governance as a Compliance Deterrent
Data integrity is often discussed as a hygiene factor, a clean-up project for the procurement operations team. It is far more powerful than that.
- When every purchase carries an unbroken lineage from initial requisition through AI-extracted contract obligation matching and final invoice reconciliation, you create a transparent deterrent.
- Employees recognize that an attempt to route a purchase outside the approved channel will be surfaced, traced to an individual, and matched against a contract that clearly does not permit it.
- The consequences of maverick spending grow heavier when the detection mechanism is visible: tool and vendor sprawl, weaker supplier use, and subscription creep become traceable to their source.
- Building this governance layer requires the AI to enrich each transaction with extracted contract clauses and the structured metadata that surrounds them.
- The system must answer a specific audit question: at the moment this purchase was made, was there a signed agreement in force that authorized it?
- The cost of creating a complex contract is $50,000, making each one a high-value asset that demands precise tracking.
- The governance layer also satisfies an increasingly aggressive regulatory environment by enabling audit-ready lineage that shifts procurement from a reactive cost center into a function that protects the enterprise from financial and regulatory blind spots.
Step 7: Measure What Matters, From Spend Reduction to Process Velocity
The old procurement scorecard leads with hard-dollar savings. That metric alone sinks AI-driven maverick spend programs. When the only thing leadership measures is cost reduction, every policy gate becomes a blunt instrument that blocks spend at any speed, frustrating business partners until they route purchases entirely outside the system.
Shift the conversation to a balanced set of KPIs that prove control and speed can coexist. The maverick spend rate (the percentage of total transaction volume flagged as off-policy) becomes your north star; drop it quarter over quarter without adding friction to legitimate purchases. Contract utilization tracks how often employees buy against a negotiated agreement instead of a one-off purchase order, a direct lagging indicator of whether your guided buying channels work. Policy exception cycle time measures how quickly a dynamic approval resolves, proving that control does not mean delay. User friction scores, gathered through simple post-purchase surveys, capture whether employees feel the new gates help or hinder them.
These metrics reorient the stakeholder conversation. When a CFO sees the maverick spend rate falling while business cycle times remain flat, the program earns funding as an enabler, not a roadblock.
A pilot delivers the proof. You can run one with a limited contract set without disrupting existing workflows, measuring these exact KPIs for a single high-risk category over a 90-day window. The data will build your business case for expansion.
Conclusion
Maverick spend control has no finish line. It runs as a continuous improvement loop that pulls together unified data, AI-driven intelligence, and proactive policy gates. The seven steps above replace reactive blocking, which employees route around, with a system where the fastest path to purchase also happens to be the compliant one.
Done right, procurement shifts from a gatekeeper that slows teams down into an enabler that protects margins and speeds operations in tandem.
Frequently Asked Questions
What is maverick spend in procurement and why is it a problem?
Maverick spend refers to purchases that employees make outside of a company’s approved procurement, finance, or expense management processes. It is a problem because it creates a blind spot for finance teams, making budgets harder to forecast and control, eroding negotiated volume discounts, and increasing risk exposure.
How can AI and procurement data be used together to detect and prevent maverick spend?
AI analyzes post-signature purchasing data, contract clauses, and vendor records to detect patterns of unauthorized buying. It flags inconsistencies between contract terms and actual invoices, clusters fragmented spend to reveal hidden consolidation opportunities, and generates risk scores that trigger proactive, guided buying interventions before maverick purchases finalize.
What key data sources and contract intelligence signals should procurement teams analyze to identify unauthorized buying?
Teams must unify three core data sources: approved vendor master data, active contract terms from a CLM system, and actual purchasing transaction logs from the ERP or P2P system. The critical signal is a mismatch where an invoice line-item lacks a corresponding active contract or an approved vendor record.
How do you build a business case and pilot an AI-driven maverick spend control initiative inside a US enterprise?
Start by diagnosing the specific breach taxonomy and sizing the exposure in a single high-risk category like SaaS subscriptions. Run a pilot on a limited contract set without disrupting existing workflows and measure pre-defined KPIs including maverick spend rate and user friction over a defined window, then present the data alongside a balanced process-velocity scorecard.
What measurable outcomes can organizations expect after deploying AI to control maverick spend?
Organizations can expect a measurable drop in the maverick spend rate, improved contract utilization, reduced policy exception cycle times, recovered volume discounts through supplier rationalization, and a transparent audit trail that cuts compliance review time from weeks to hours.
How does an AI intelligence layer compare to traditional CLM or ERP approaches for post-signature spend compliance?
Traditional tools enforce policy reactively at the point of entry. An AI intelligence layer analyzes post-signature patterns and contract signals to detect unauthorized buying, enabling proactive policy enforcement without the hard blocks that employees circumvent, and without requiring a replacement of existing CLM and ERP investments.