Introduction
Your CFO just discovered $450,000 in software subscriptions no one knew existed, paid for with a dozen different corporate cards and tied to zero approved vendor contracts. The renewal dates are scattered across three departments, and nobody owns them. This is modern maverick spend. Rogue stapler purchases and client lunches expensed at the wrong restaurant are the minor-league version. In 2026, off-contract purchasing is a structured, scalable threat that leaks savings, weakens supplier use, and exposes the business to security and legal risk, all while hiding in plain sight inside fragmented ERP and credit card data.
The traditional response has been reactive: a periodic audit that finds the mess months after the money left the bank, followed by a sternly worded policy memo and a hope that it will not happen again. That approach is failing. Employees bypass approved vendor contracts because the compliant path is slow, confusing, or buried in a tool nobody wants to open. Stopping maverick spend now demands a shift from a policing mindset to a governance model that is continuous, automated, and intelligent. This article outlines the six-step system that moves your organization from data blindness to real-time, AI-powered enforcement, so that every transaction either matches an approved contract, or it raises a flag before you pay for it.
Key Takeaways
The six steps below convert maverick spend from a hidden liability into a managed, solvable problem.
- Unify Your Data: Ingest all card transactions, POs, invoices, and contract terms into one layer. A platform like Suplari can unify this spend data into a single intelligence layer within 30 days, eliminating the silos where maverick spend hides.
- Monitor in Real Time: Replace quarterly audits with continuous scanning. AI agents detect unauthorized purchases and off-contract transactions within hours.
- Diagnose the Root Causes: Move beyond blaming buyers. Analyze violation patterns to fix the slow approvals, unclear policies, and poor tool UX that drive users to bypass contracts.
- Embed Compliance Gates: Insert dynamic, risk-based approval thresholds and automated contract matching into the purchase-to-pay workflow to stop noncompliant spend before it completes.
- Activate an AI Intelligence Layer: Deploy a post-signature governance layer that classifies risk, spots anomalies, and triggers remediation at transaction speed, without requiring a rip-and-replace of your ERP.
- Measure Real Compliance: Track the percentage of on-contract spend, the volume of detected maverick transactions, and the speed of violation detection shifting from months to hours.
Step 1: Unify Your Spending and Contract Data into a Single Source of Truth
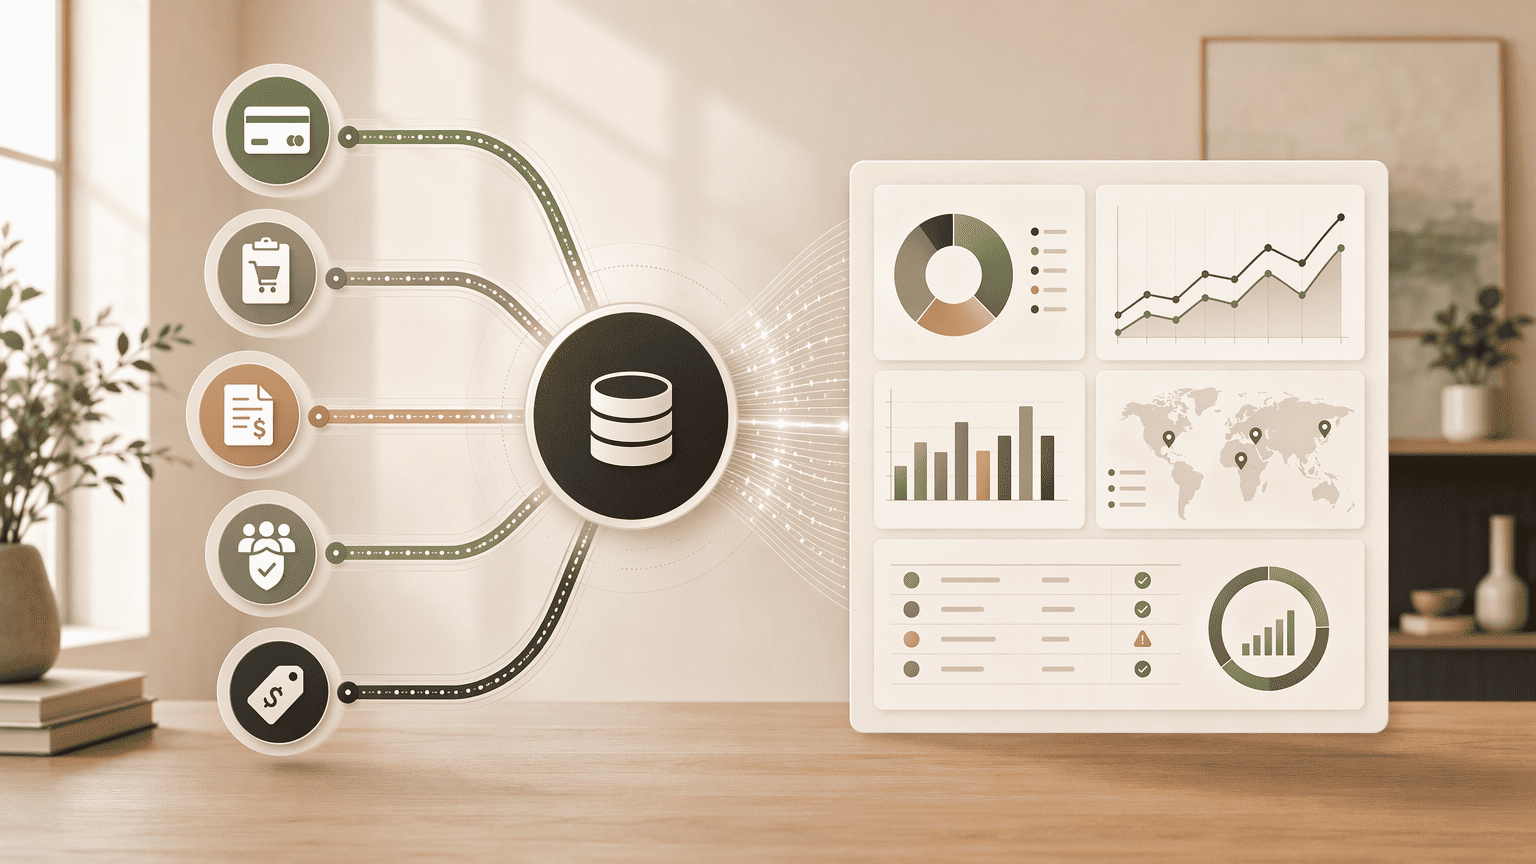
Fragmented data is the root enabler of maverick spend. Until your card transactions, POs, and invoices sit in the same view as your approved vendor lists and negotiated pricing, you are effectively blind to the leakage. This step replaces reactive audits with a foundation for always-on visibility.
| Data Domain | Traditional Fragmented State | Unified State Goal |
|---|---|---|
| Spend Transactions | Card feeds, POs, and invoices scattered across ERP modules, bank portals, and spreadsheets. | All transactional data ingested into a single intelligence layer, normalized to a common taxonomy. |
| Contract Intelligence | Key pricing, vendor, and renewal terms locked in static documents, PDFs, and shared drives. | Active contract metadata extracted and linked to transactional records, surfacing negotiated vs. actual pricing. |
| Supplier Master | Duplicate supplier records, multiple names for the same vendor, and uncategorized tail spend. | Supplier unification with a clean, AI-ready data foundation that classifies spend to L3+ depth within 90 days. |
| Time to Visibility | Quarterly or annual manual consolidation projects that take weeks to reconcile. | A unified foundation delivered within 30 days, enabling continuous monitoring from day one. |
Getting to a single source of truth means you stop discovering off-contract purchases during a year-end scramble. You make the compliance question answerable with a query.
Step 2: Deploy Continuous, Real-Time Monitoring Against Active Contracts
The defining shift in 2026 is the move from periodic spot checks to a system that catches violations in flight. You cannot fix what you learn about nine months after the invoice was paid.
A quarterly audit is a post-mortem. It explains what went wrong after the cash is spent. Jon Stegner, whose team at Delphi caught an estimated 80% or more of maverick spend, ran a model where internal auditors checked purchasing decisions.
Platforms like Suplari flip the model by running AI agents and Digital Workers against every transaction. They compare each purchase to active contract terms, approved vendor lists, and policy thresholds the moment it enters the system. Within hours of an off-contract software subscription or a out-of-policy travel expense appearing in AP, the agent flags it and assembles audit-ready documentation.
The real prize is a window to act. Flag a maverick transaction today, and you can stop the 12-month SaaS auto-renewal or the rogue supplier invoice tomorrow, before either clears a batch payment run. You stop being a financial historian and start controlling spend in real time. Suplari’s continuous compliance monitoring runs this scan at the speed of your payables, delivering what point-in-time sampling never could.
Step 3: Diagnose and Remediate the Root Causes, Not Just the Transactions
Catching and killing off-contract purchases fixes the symptom. Effective governance analyzes violation patterns to answer a harder question: why did a reasonable employee bypass a negotiated contract in the first place? Start here.
- Map Violation Patterns to Friction Points: Aggregate detected maverick transactions and categorize them by department, spend category, and vendor type. Cross-reference the findings to reveal whether off-contract buying spikes correlate with a specific approval workflow that takes three extra days, or a procurement tool that is universally despised for its complexity.
- Interview the Bypassers Directly: Select a sample of employees who made low-risk maverick purchases and ask a single, open-ended question: what made the compliant path feel harder than this one? The answers will almost always cluster around unclear policies, perceived slowness, or a purchasing process that feels designed for million-dollar capital equipment while someone just needs a recurring $200 software tool.
- Redesign the Compliant Path to Be the Easiest Path: Take the top friction insight and rewrite the process. This might mean creating a fast-lane, pre-approved catalog for common sub-$5,000 purchases, or embedding a purchase request directly into the collaboration tool employees already live in. You make staying on contract effortless.
- Close the Awareness Gap with Active Guidance: Deploy a real-time nudge at the moment of a suspicious transaction: a message that says, “You are purchasing from an unapproved vendor. An approved supplier for this category is available at a better price here,” with a one-click redirect. Turn detection into education, instantly.
Step 4: Embed Intelligent Compliance Gates into the Purchase-to-Pay Workflow
Real-time monitoring detects violations after a transaction is initiated. The next stage of maturity is preventing the noncompliant purchase from completing at all, by embedding dynamic, risk-based controls directly into your purchase-to-pay (P2P) workflow. You are adding intelligence exactly where it is needed, right before money leaves the business.
You do this by configuring approval thresholds that scale with the risk of the spend. A $50 desk organizer from an uncategorized vendor routes for a single automated email notification. A $50,000 services engagement from an unapproved firm triggers a mandatory approval chain with contract matching. Mercury.com highlights two maverick triggers that get blocked at the point of purchase when the payment rail itself queries the contract database before authorizing the charge: undocumented card transactions and unapproved software subscriptions.
The goal is a system that says “yes” fast for low-risk, policy-aligned purchases and “no, with guidance” for transactions that fall outside approved parameters. By inserting automated contract matching at the point of purchase, you offload the policing burden from managers and auditors and bake it into the transactional pipes. A department head trying to swipe a corporate card for a tool that already has an enterprise license gets redirected to the compliant supplier in real time, never learning that the maverick option exists. You have made the correct choice invisible and automatic.
Step 5: Harness an AI-Powered Intelligence Layer for Post-Signature Governance
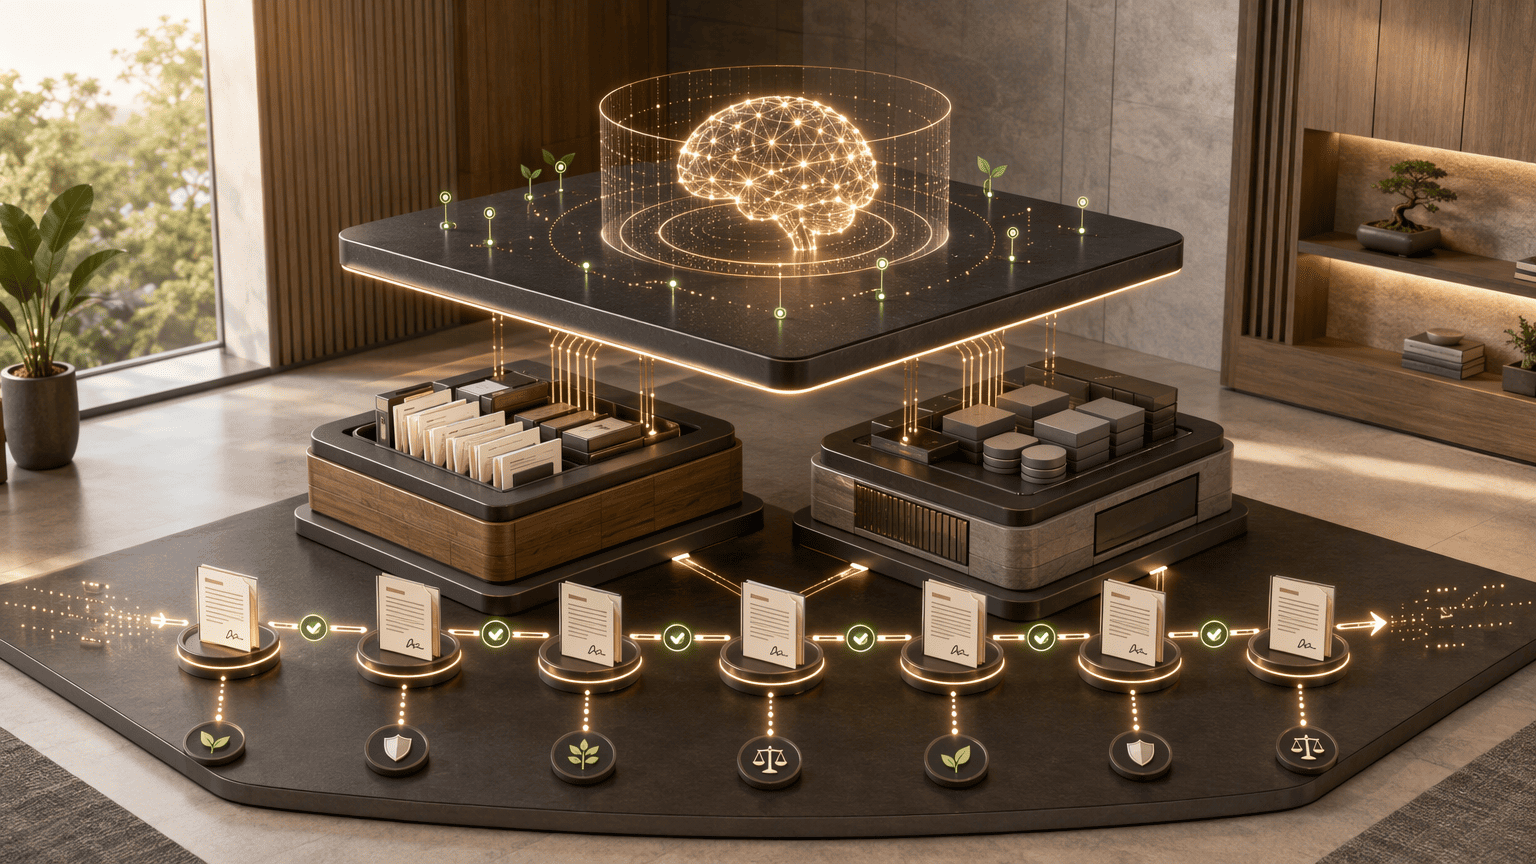
A traditional CLM or ERP checks rules periodically and requires someone to define those rules upfront. An AI intelligence layer operates differently because it learns and acts continuously, at the speed of each transaction.
After your contracts are signed, the work of protecting their value has just begun. Legacy CLM systems are designed for pre-signature workflows: authoring, negotiation, and approval. They are rarely equipped to govern the complex, messy reality of hundreds or thousands of transactions flowing against those contracts every day. An AI-powered intelligence layer continuously classifies every transaction’s risk, detects anomalies that no static rule would catch, and triggers automated remediation workflows. If a department’s spending on a category suddenly shifts mid-quarter from a preferred supplier to a pattern of small, fragmented purchases, the AI flags that behavior shift.
This matters because post-signature governance must be as intelligent as the strategic sourcing that came before it. You negotiated a hard-won discount based on volume, then watched it evaporate. The AI layer protects that negotiated outcome every day.
Step 6: Measure Success with the Metrics That Signal True Compliance
You cannot manage what you do not measure, but most procurement metrics track activity, not protection. For maverick spend, the right KPIs shift the scoreboard from the volume of audits completed to the speed and coverage of your defense.
- Compliant spend percentage: Track the percentage of total spend that is compliant against active contracts. A rising number here reflects the system’s effectiveness, not just the team’s diligence.
- Maverick transaction volume and value: Pair the volume and value of maverick transactions detected, tracked over time to reveal whether root-cause fixes are actually reducing the attempts. Delphi’s experience of catching an estimated 80% or more of maverick spend sets a practical benchmark for what a mature detection framework can achieve, but you must also define what you will not chase, Stegner’s team consciously set a threshold of not testing for spend under $50,000, a pragmatic boundary that keeps the program focused on material leakage.
- Mean time to detect (MTTD): The shift from finding an off-contract purchase in a quarterly audit (270-plus days) to an AI agent flagging it within hours represents a change in operational capability. When your MTTD drops to a single-digit number of hours, you have moved from controlling historical damage to governing in real time.
Your compliance function stops being a post-mortem analyst and becomes a living immune system.
Conclusion
Stopping maverick spend is a data, workflow, and intelligence design challenge, and the technology to solve it has reached a tipping point. The six steps outlined here form an integrated system: unify your data to gain visibility, deploy AI agents to catch leakage in real time, diagnose and fix the friction that drives bypassing, embed automated compliance gates, and activate a persistent intelligence layer that protects every negotiated contract. The 2026 standard is autonomous, continuous governance. You can have full visibility and ironclad compliance without slowing down a single legitimate business purchase.
Frequently Asked Questions
What is maverick spend and why does it happen despite having approved vendor contracts?
Maverick spend refers to purchases that employees make outside of a company’s approved procurement, finance, or expense management processes. It persists because the compliant path often feels slower or more complex. Common root causes include unclear spending policies, cumbersome approval workflows, and poor adoption of procurement tools that push employees toward faster, unauthorized alternatives.
What are the financial and operational risks of unchecked maverick spending in 2026?
Unchecked maverick spending directly erodes the value of your negotiated agreements through several mechanisms:
- Value erosion: It erodes the value of your negotiated agreements.
- Vendor and tool sprawl: It causes tool and vendor sprawl, weakening your supplier use by fragmenting volume.
- Subscription creep: It creates subscription creep from unmanaged renewals.
- Risk exposure: It exposes the business to higher legal and security risks from unvetted vendors.
- Forecasting noise: It injects noise into financial forecasting.
How can organizations detect contract leakage and off-contract purchasing in real time?
You detect leakage by deploying a continuous monitoring system that scans every transaction at the moment it occurs. AI agents and Digital Workers cross-reference card charges, POs, and invoices against your active approved vendor lists and contract terms, flagging unauthorized purchases within hours instead of waiting for quarterly manual audits.
What steps can procurement and finance teams take to enforce contract compliance without slowing down the business?
To reduce maverick spend, follow these three steps:
- Unify data: Start by unifying all spend and contract data into a single source of truth.
- Embed intelligent gates: Then embed intelligent compliance gates that auto-approve low-risk, on-contract purchases instantly while routing high-risk exceptions for a fast review.
- Remove workflow friction: Continuously diagnose and remove the workflow friction that forces employees to bypass the compliant path.
How does an AI-powered intelligence layer help stop maverick spending compared to traditional CLM or ERP enforcement?
A traditional CLM or ERP enforces static rules at scheduled intervals or at a few checkpoints. An AI intelligence layer operates continuously, classifying the risk of every single transaction, detecting anomalous spending patterns, and triggering remediation automatically, without requiring you to pre-define every possible violation scenario upfront.
How should a company measure the success of a maverick spend reduction initiative?
Track these three KPIs:
- Compliant spend percentage: The percentage of total spend that is compliant against active contracts.
- Maverick transaction reduction: The year-over-year reduction in volume and value of flagged maverick transactions.
- Mean time to detect (MTTD): The critical shift is moving MTTD from months in a quarterly audit cycle to hours under a continuous monitoring model.
Sources
- Compliance Intelligence to Monitor Continuously, Not Audit Annually | suplari – suplari.com
- What is maverick spend? How to identify — and how to reduce it | Mercury – mercury.com
- Managing Maverick Spend at Deere and Delphi – An Interview with Jon Stegner | Supply Chain Resource Cooperative – scm.ncsu.edu